A tamper-evident audit record for every governed decision
ARIA is designed to capture compliance-relevant evidence at the point of decision — what happened, when, under which rules, and that nothing was changed afterward — rather than reconstructing it after the fact.
This runs entirely in your browser using the Web Crypto API — nothing is sent anywhere. It illustrates the same one-way, tamper-evident hashing principle ARIA applies to decision records, not ARIA itself.
What ARIA is
ARIA is a deterministic behavioural intelligence substrate — it observes operational and behavioural signals, evaluates them against transparent, versioned rules, and produces a governed decision together with a verifiable record of how that decision was reached. The same inputs always produce the same outputs, and the reasoning behind every decision is inspectable after the fact.
What it does
Records, doesn't decide
ARIA is non-agentic. It captures and verifies evidence about governed decisions — it does not make those decisions itself.
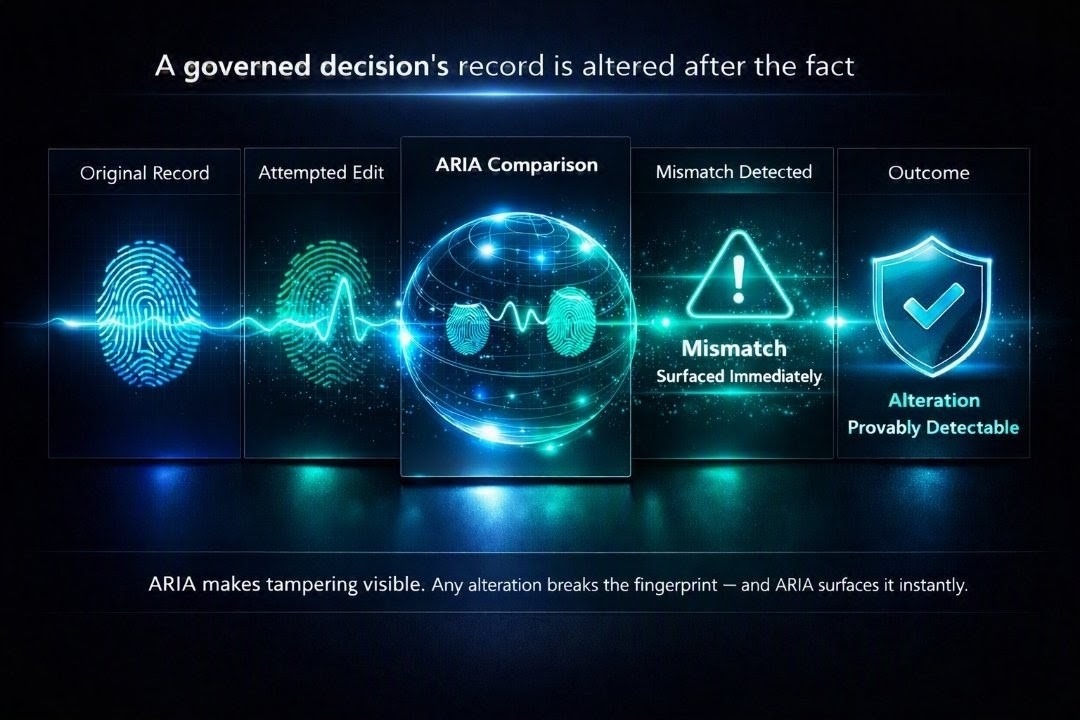
Tamper-evident by construction
Records are cryptographically hashed and can be anchored externally, so any after-the-fact alteration is detectable, not merely disallowed by policy.
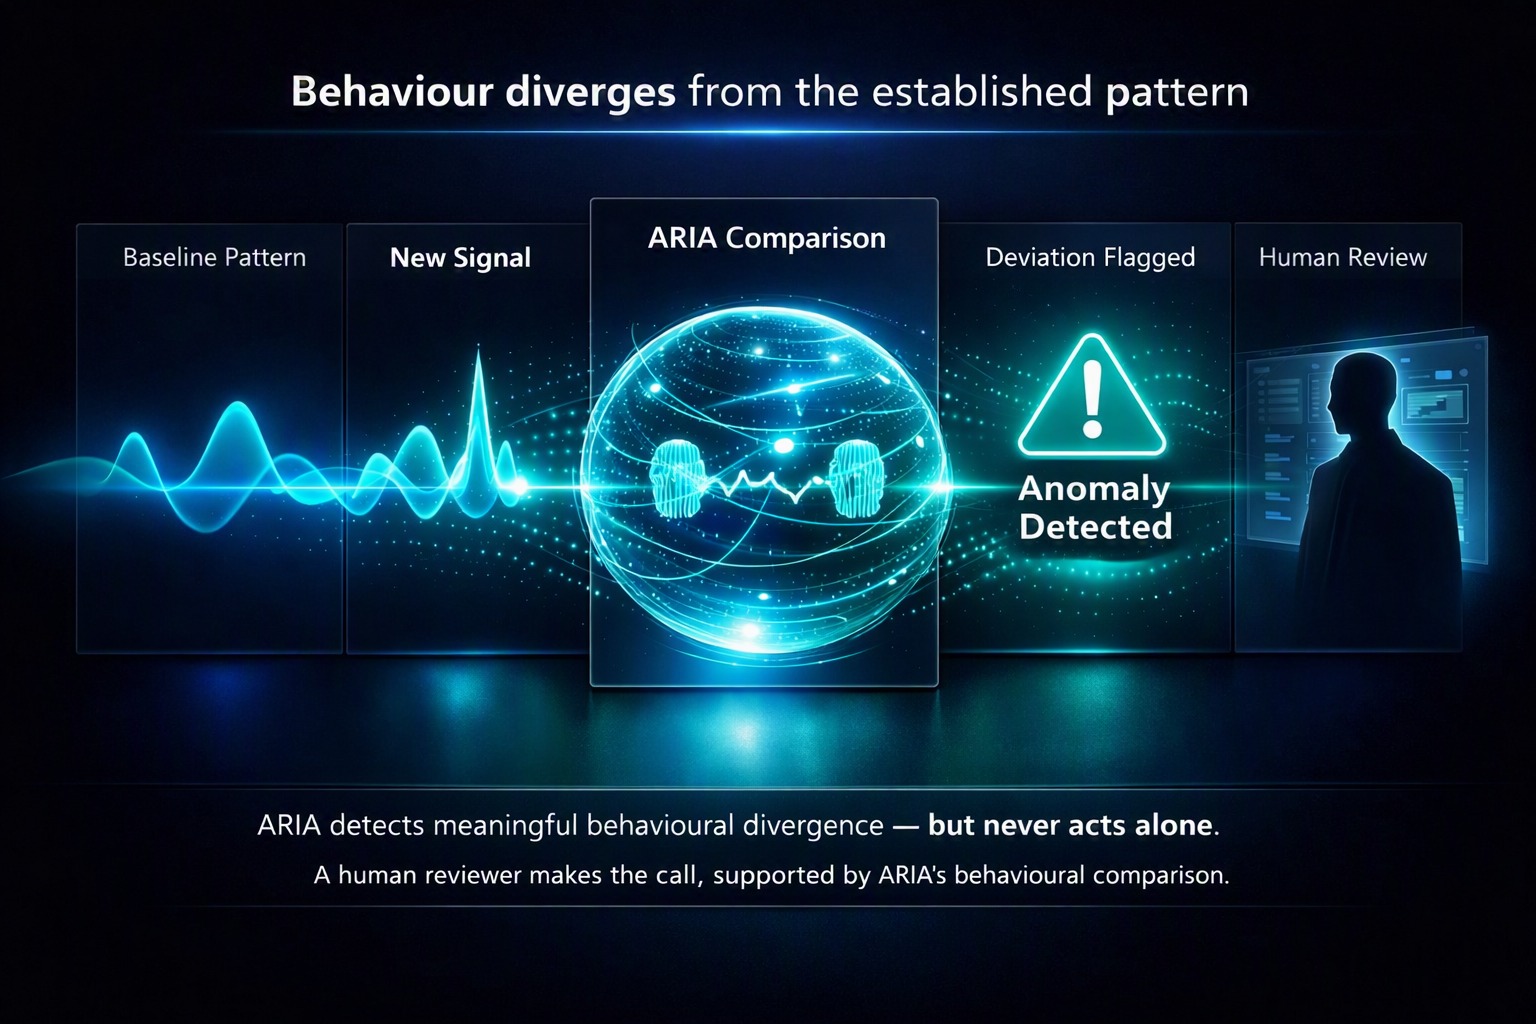
Flags drift, doesn't act on it
Part of that evaluation includes comparing current behaviour against an established baseline and surfacing meaningful deviation to a human reviewer — ARIA flags, it never acts automatically.
Built for OEM licensing
Designed as a substrate other products integrate into their own governed workflows — not a standalone end-user application.
Domains with shipped taxonomy
ARIA ships with working signal definitions, regulatory mappings, and escalation tiers for these sectors, tested and wired into production signoff.
Scoped, in progress
Draft taxonomy and threshold structures exist for these sectors as a starting point. Signoff logic is engineered per vertical during onboarding, the same process Financial and Safeguarding went through.
Not your sector? Register your vertical and we'll scope a taxonomy with you. Full capability detail →
How it responds
A returning user's behaviour changes
A record is altered after the fact